The ARIANNA platform

One platform for the whole vulnerability management process

ARIANNA builds one model per device design, checks it against new vulnerabilities every day, and guides your teams from triage to audit-ready evidence, for every firmware version in the field.

Book a free demo

Five integrated capabilities

  1. 01
    Device Model creation & managementSBOM, HBOM & Security Context in one model.
  2. 02
    Continuous monitoring & intelligenceVulnerability Assessment Report & Data Enrichment updated daily.
  3. 03
    Automatic assessmentVulnerability Prioritisation, Patch intelligence, False Positive detection, Exploitability analysis.
  4. 04
    Triage and remediation trackingFrom triage to closure, every analysis & decision fully traceable.
  5. 05
    Reporting & Audit-ready evidenceEvidence for customers, auditors and regulators.
SBOM & HBOM

A complete model of your device

Everything starts with the Device Model: one per device design, with its hardware (HBOM) and software (SBOM) in one place.
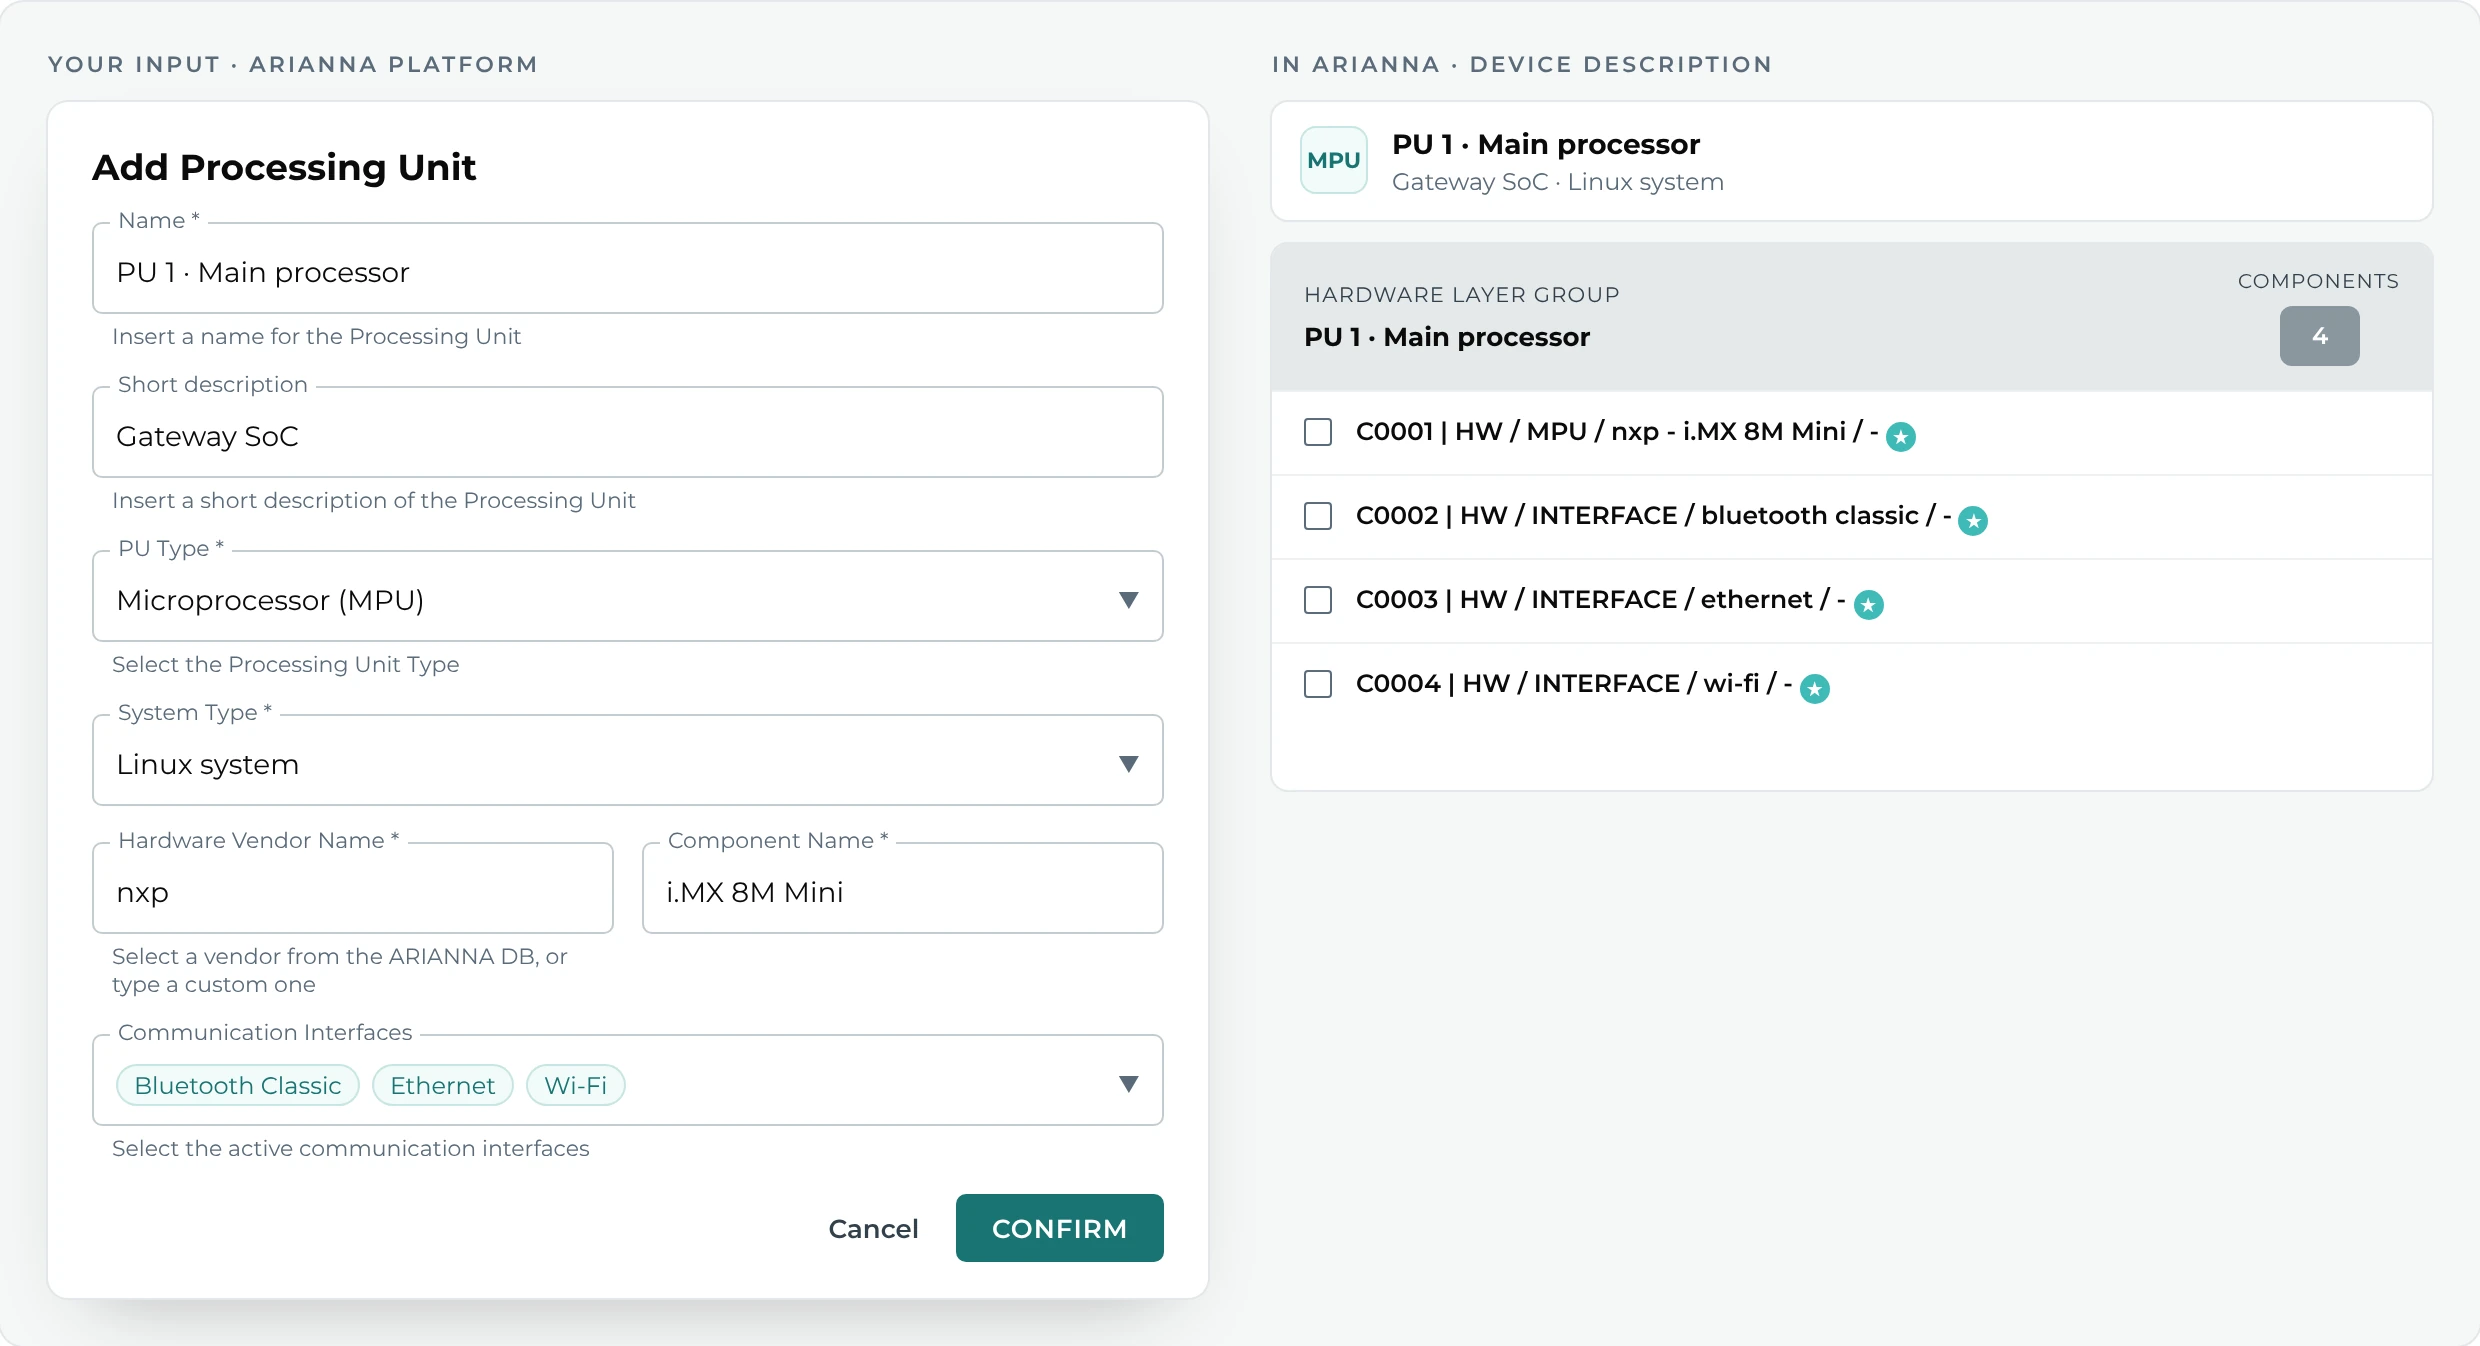
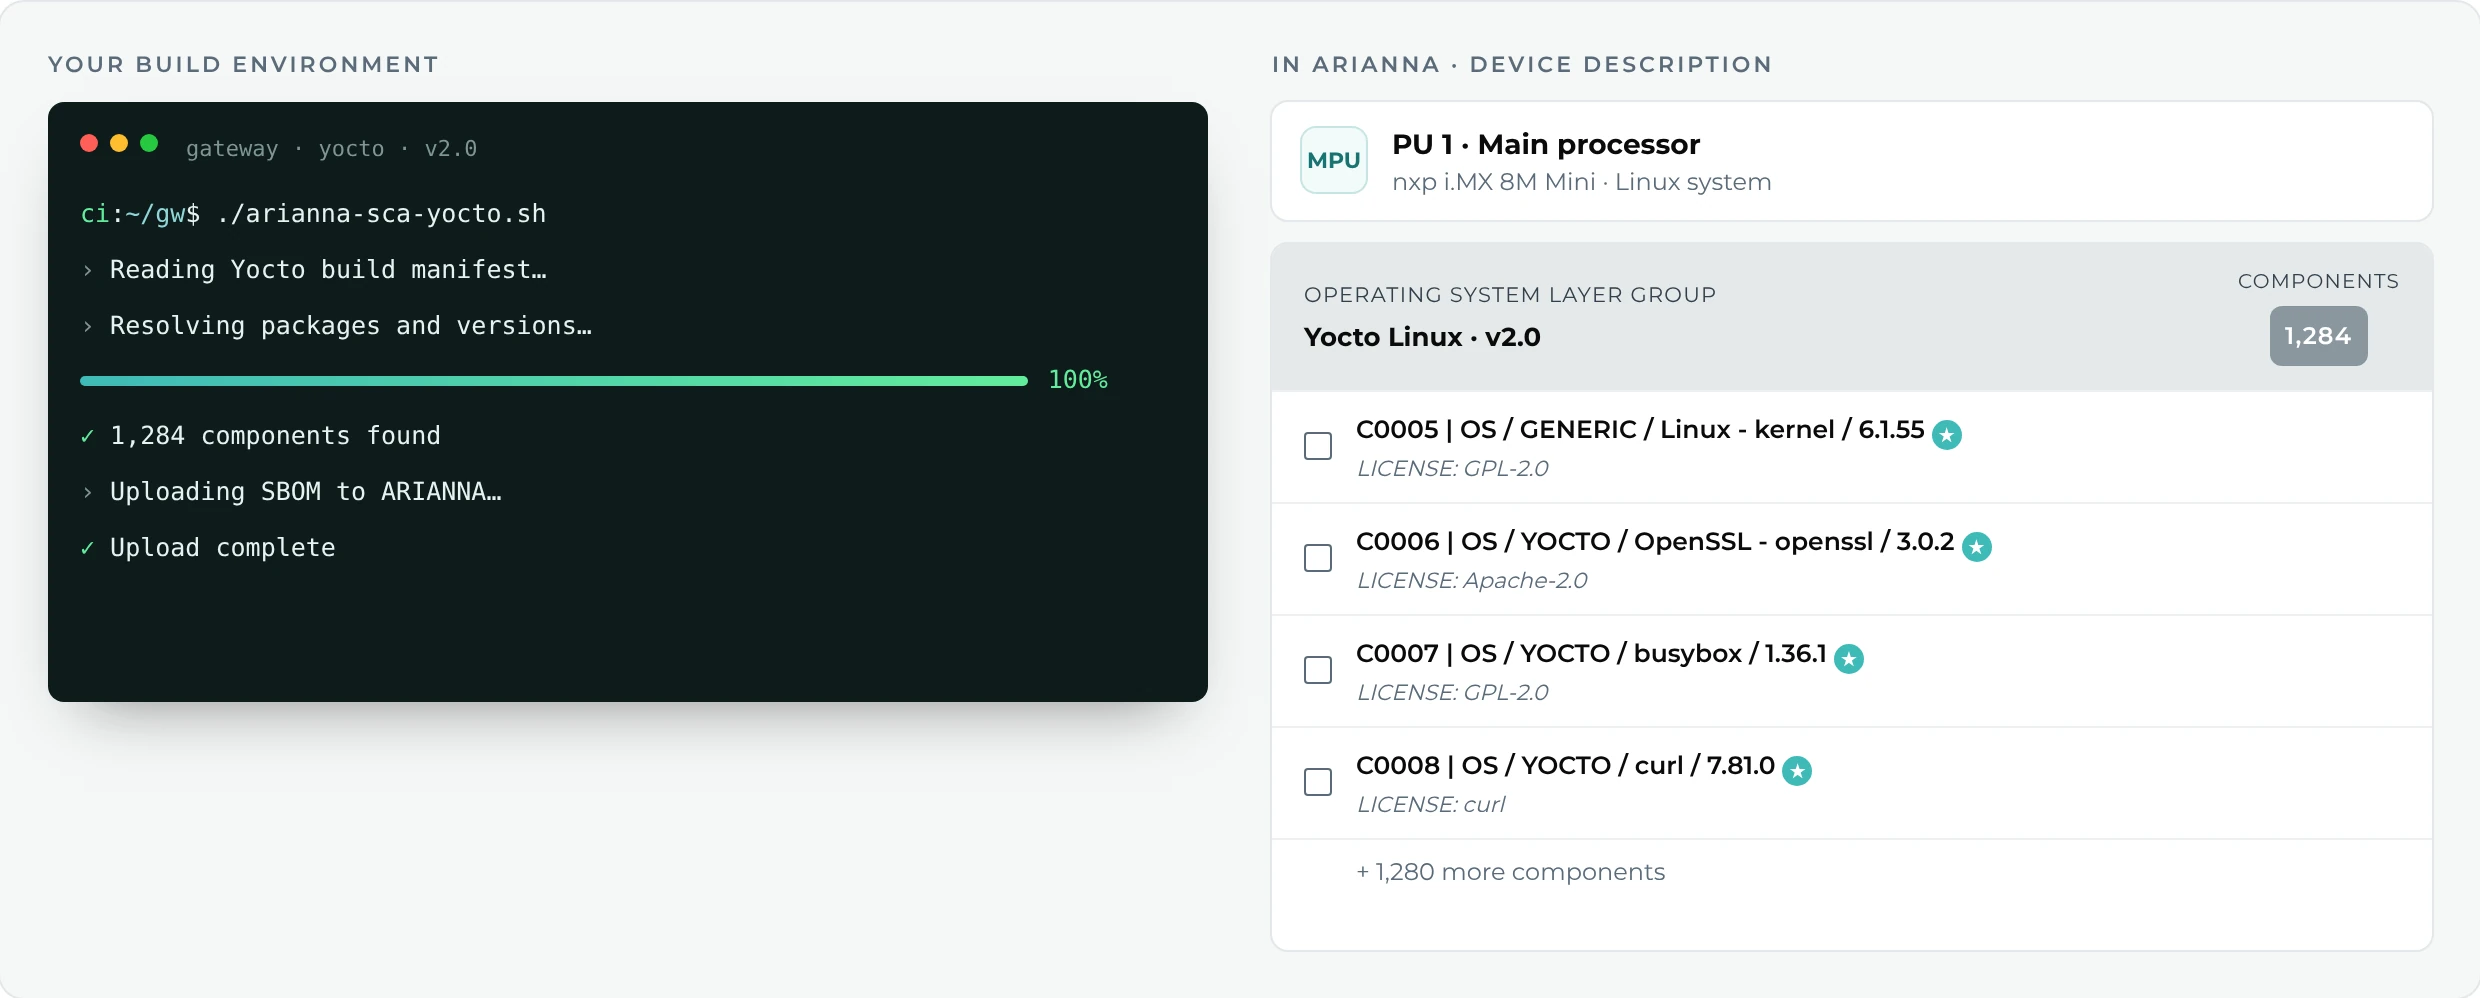
Organised like your architecture. Every MCU, MPU, secure element and module, each with its own components and interfaces.
One version per firmware release. Existing triage decisions and assessments carry over, while vulnerabilities affecting components that have been removed or updated are automatically closed when no longer applicable.
ARIANNA: Add Processing Unit form filled in for an NXP i.MX 8M Mini running Linux, with the resulting hardware layer group: processor plus Bluetooth Classic, Ethernet and Wi-Fi interfaces.
Add a processing unit: pick the vendor and component from the ARIANNA database and select its interfaces. The hardware layer group fills in.
ARIANNA SCA tool run on a Yocto build: 1,284 components found and uploaded, shown in the operating system layer group.

The SCA tool runs in your build and uploads the SBOM. Every software component lands in its layer group.

SCA tools

Accurate SBOMs, straight from your build

ARIANNA's own Software Composition Analysis tools are lightweight scripts (Python, Bash or PowerShell) with no external dependencies. Run them on their own or inside your CI/CD pipeline.

The most accurate SBOM, without sharing your code. No guessing from binaries, so no missing components or wrong versions. You keep full control of your proprietary software.
CI/CD pipeline integration. Run the tools after each release; results upload through the REST API and start a new assessment.

One tool per technology stack

Operating systems
YoctoBuildrootOpenWRTDebianUbuntuAlpineRed HatGentooAndroidWindows
MICROCONTROLLERS FIRMWARE
ZephyrSTM32 SDKEspressif SDKNXP SDKNordic SDKSilicon Labs SDKTexas Instruments SDKMicrochip SDKIAR EWKeilOther RTOS
Applications, cloud & containers
C/C++C#.NETGoJavaGradleMavenJavaScriptPHPPythonRustCloud & containers
Continuous monitoring

Every component, checked every day

Every component is checked daily against ARIANNA's vulnerability database, built from public sources and curated by our security team.

Daily vulnerability mapping. Every component is mapped to new vulnerabilities each day, so you stay in control of your security posture and, thanks to our prioritisation filters, know what to address first.
Vulnerability enrichment. Exploitation data from CISA KEV and ENISA EUVD, canary and honeypot systems, and ARIANNA's own verified intelligence.

Vulnerability sources

NIST NVDNational Vulnerability Database
CVE.orgMITRE CVE programme
GitHub Security AdvisoriesOpen-source ecosystems
ENISA EUVDEuropean Vulnerability DatabaseExploitation alerts
Automatic assessment & prioritisation

Focus on the most important vulnerabilities first

Before your team looks at anything, ARIANNA removes what doesn't apply and ranks the rest. Final decisions always stay with your security experts.
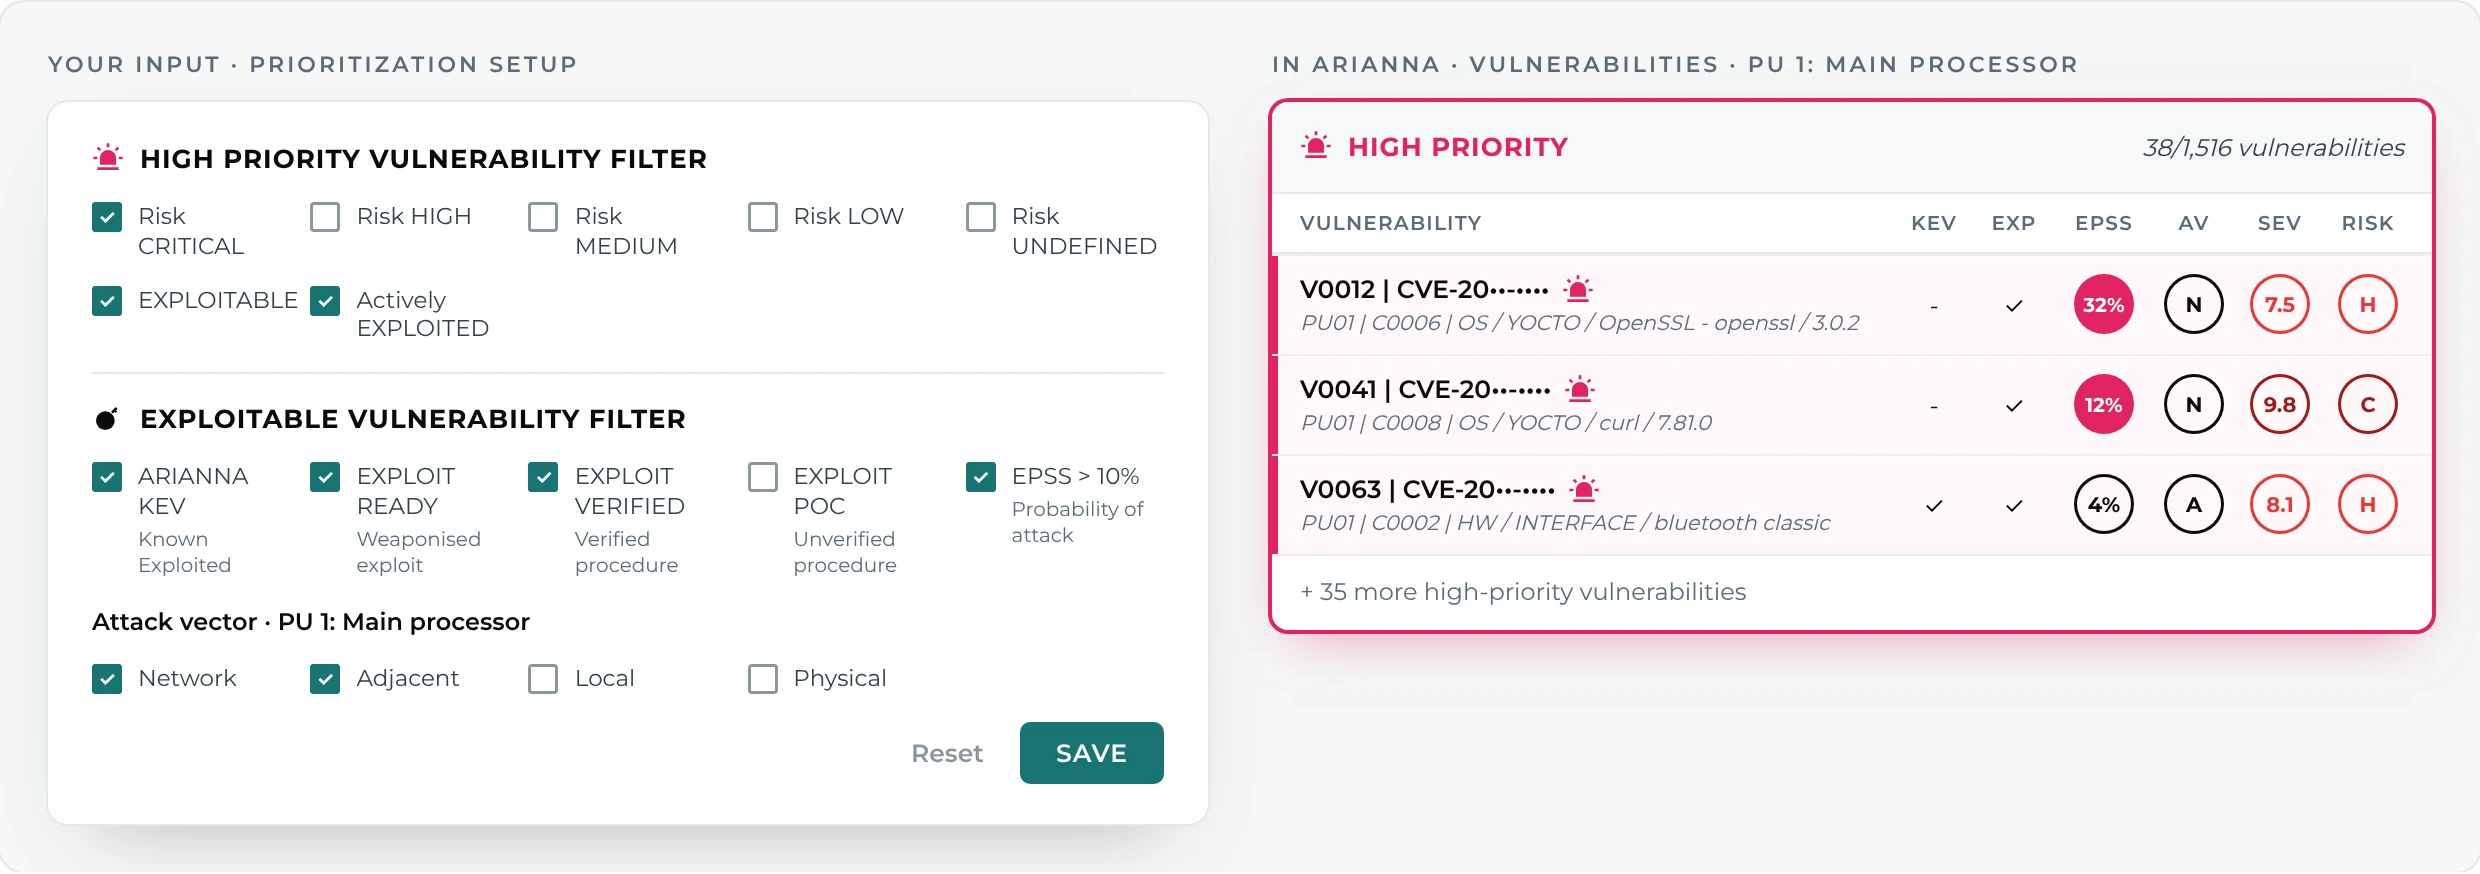
Automatic applicability analysis. When the vulnerable version is removed, updated or patched in the build, findings are adjusted or discarded automatically.
Pre-triage & prioritisation engine. Every open vulnerability is marked High or Low priority by your own rules, either risk-based or exploitability-based.
ARIANNA prioritisation setup and the resulting high-priority list: 38 of 1,516 vulnerabilities.
Set once what high priority means. ARIANNA applies it to every vulnerability: 38 of 1,516 left to fix first.
Remediation & policies

A clear path from triage to closure

A four-stage pipeline covers the whole life of a vulnerability. Every status change, note and risk update is recorded, so each decision is traceable in an audit.
Four stages, one pipeline. From identification and triage to addressing, and finally closing or disclosing each vulnerability.
Deadlines by risk level. Set from your policies or contracts, with reminders before they expire.
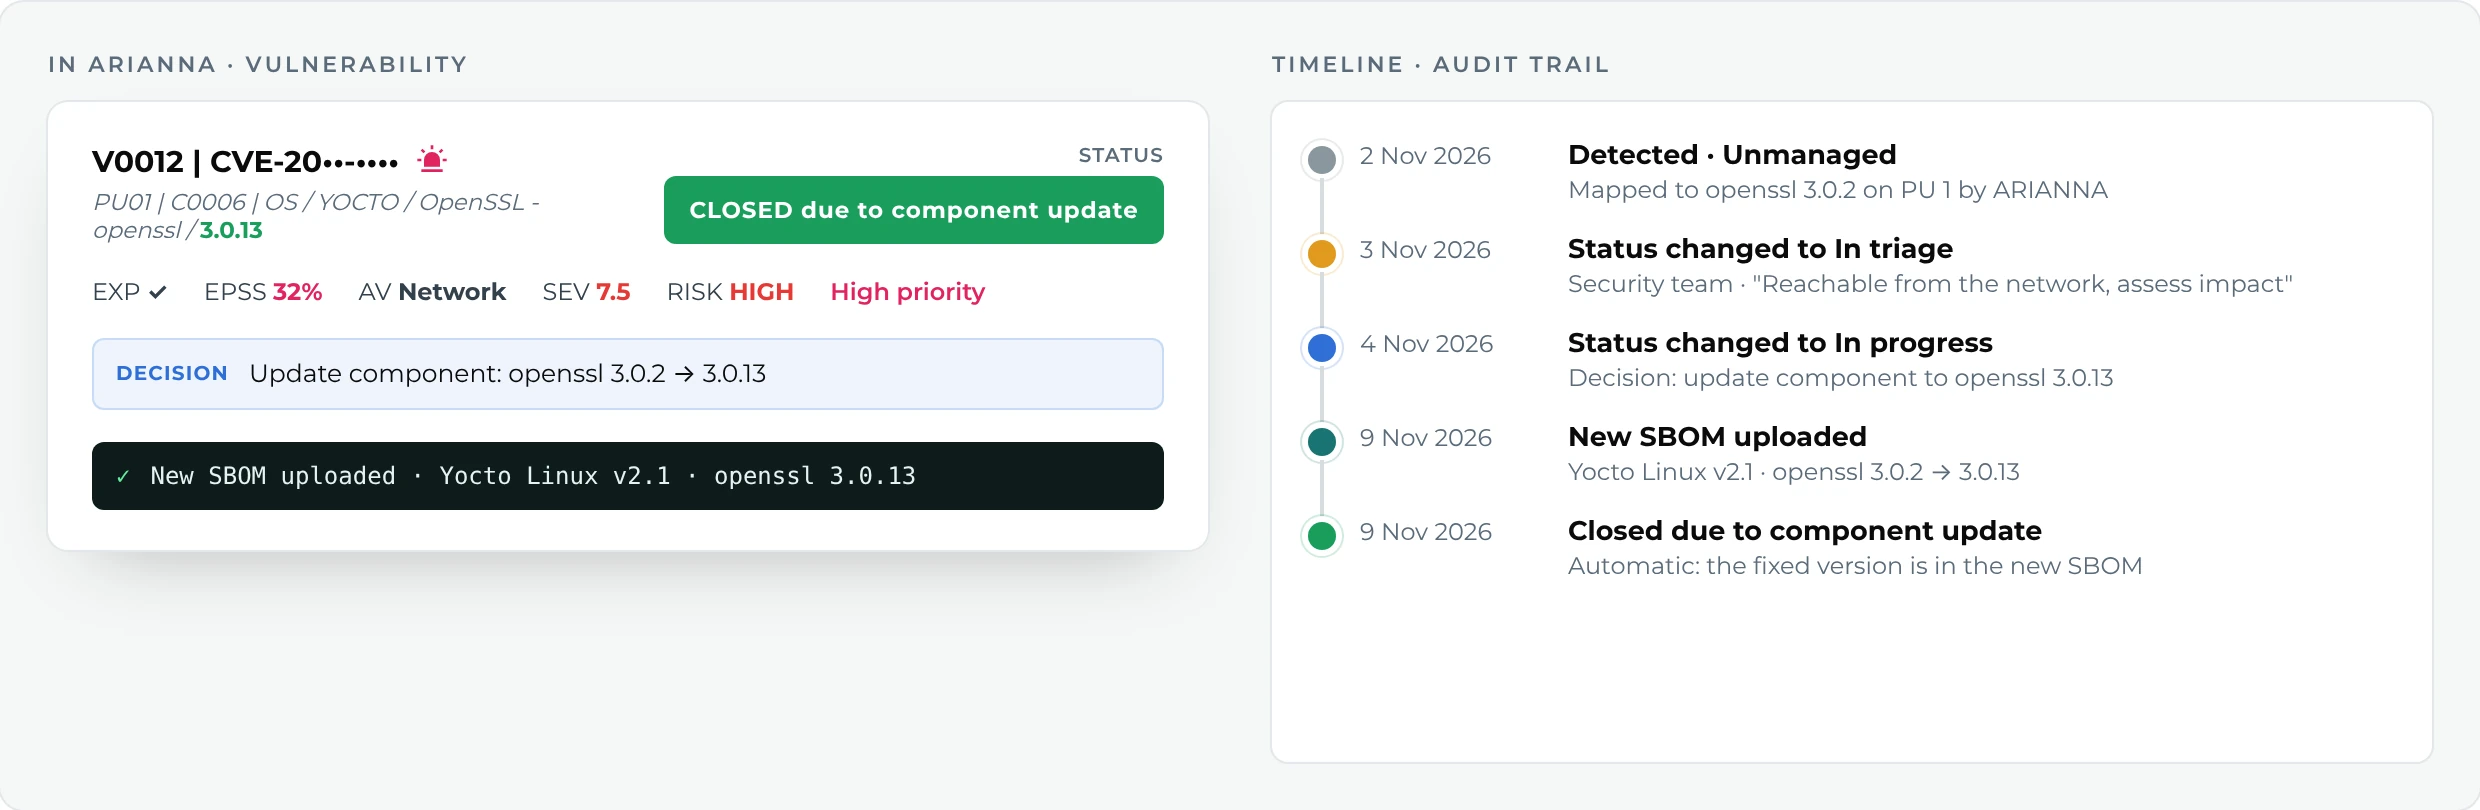
Automatic closure. A firmware update that fixes the component closes the vulnerability.
ARIANNA vulnerability with status Closed due to component update, and its timeline from detection to closure.
Every status change is recorded. When a new SBOM contains the fixed version, ARIANNA closes the vulnerability automatically.
Reporting & exports

Reach compliance with ease

A daily report with open and closed vulnerabilities, risk over time, and what's new or overdue.

Exports in your preferred format. Machine-readable formats to support your security and compliance tools or team.

Export formats

CycloneDXSPDXVEXPDFCSV
Integrations & API

Fits the way your teams already work

Product security works in ARIANNA; developers keep their own tools. Both stay in sync.

Issue trackers (Jira, Redmine, GitHub Issues). Send a vulnerability to development with the affected component, severity, recommended fix and advisories. Status syncs back, and the security team is told when the issue closes.
CI/CD & REST API. Run the SCA tools in your pipeline after each release, upload the result through the REST API, and start a new assessment automatically.
Plans

From one product in development to a full portfolio

Every plan includes the full platform, SCA tools, hardware catalogue, prioritisation, vulnerability management, exports and unlimited users.

On-demand assessment

Essential

Assessment reports whenever you need them, using tokens. Best for products in development, simple devices and products not yet in regulatory scope.

Continuous assessment

Professional

Daily monitoring and reports for products on the market that must comply with the CRA, RED and IEC 62443. Licensed per device platform, from 1 to 25.

Centralised governance

Enterprise

Everything in Professional with unlimited device platforms on a dedicated instance, for central product security teams running many products.

Book a free demo We'll help you pick the right plan for your portfolio.